
Bristol Airport powered by ransomware attack
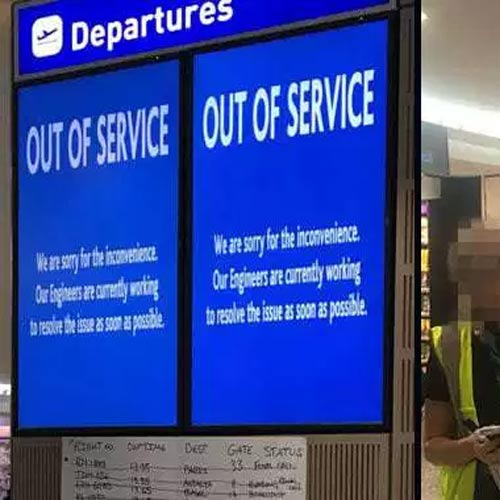
With the high powered ransom attack in the airport for non-working flight information screens at Bristol Airport in the UK over the weekend falling the victim of cyber attack, which affected the display screens
When travellers at Bristol Airport in the U.K. looked at flight information screens over the weekend, they saw a blue screen with white lettering that stated and the screens were pulled offline in the early hours of Friday after a ransomware attack crippled arrival and departure boards.
Officials for the U.K. airport blamed it on a ransomware attack. Arrival and departure information was instead posted on whiteboards and announced over the public speaker system over the weekend. The spokesman said no "ransom" had been paid to get the systems working again.
The indications are that this was a speculative attempt rather than a targeted attack on Bristol Airport. No flights were disrupted, though it is unlikely they were able to do anything about the annoying fanfare when Ryanair planes land.
The way adoption of IoT is coming up, the risk increases are in very common. IoT means (IT and OT). When the malware /ransomware hits the IT, it can still manage the infrastructure, but when it impacts the OT then it becomes very dangerous task. Hence, the security head need to understand the technicality issues.
In the statement, from the airport, we believe there was an online attempt to target part of our administrative systems and that required us to take a number of applications offline as a precautionary measure, including the one that provides our data for flight information screens. That was done to contain the problem and avoid any further impact on more critical systems. The crisis had handledwith the help of whiteboards ,which were on standby for deployment in the Bristol incident but were ultimately not required.

See What’s Next in Tech With the Fast Forward Newsletter

Tweets From @varindiamag
Nothing to see here - yet
When they Tweet, their Tweets will show up here.